Give your employees the AI they're asking for, on infrastructure you control.
GRACE is built for the rules public institutions live by.

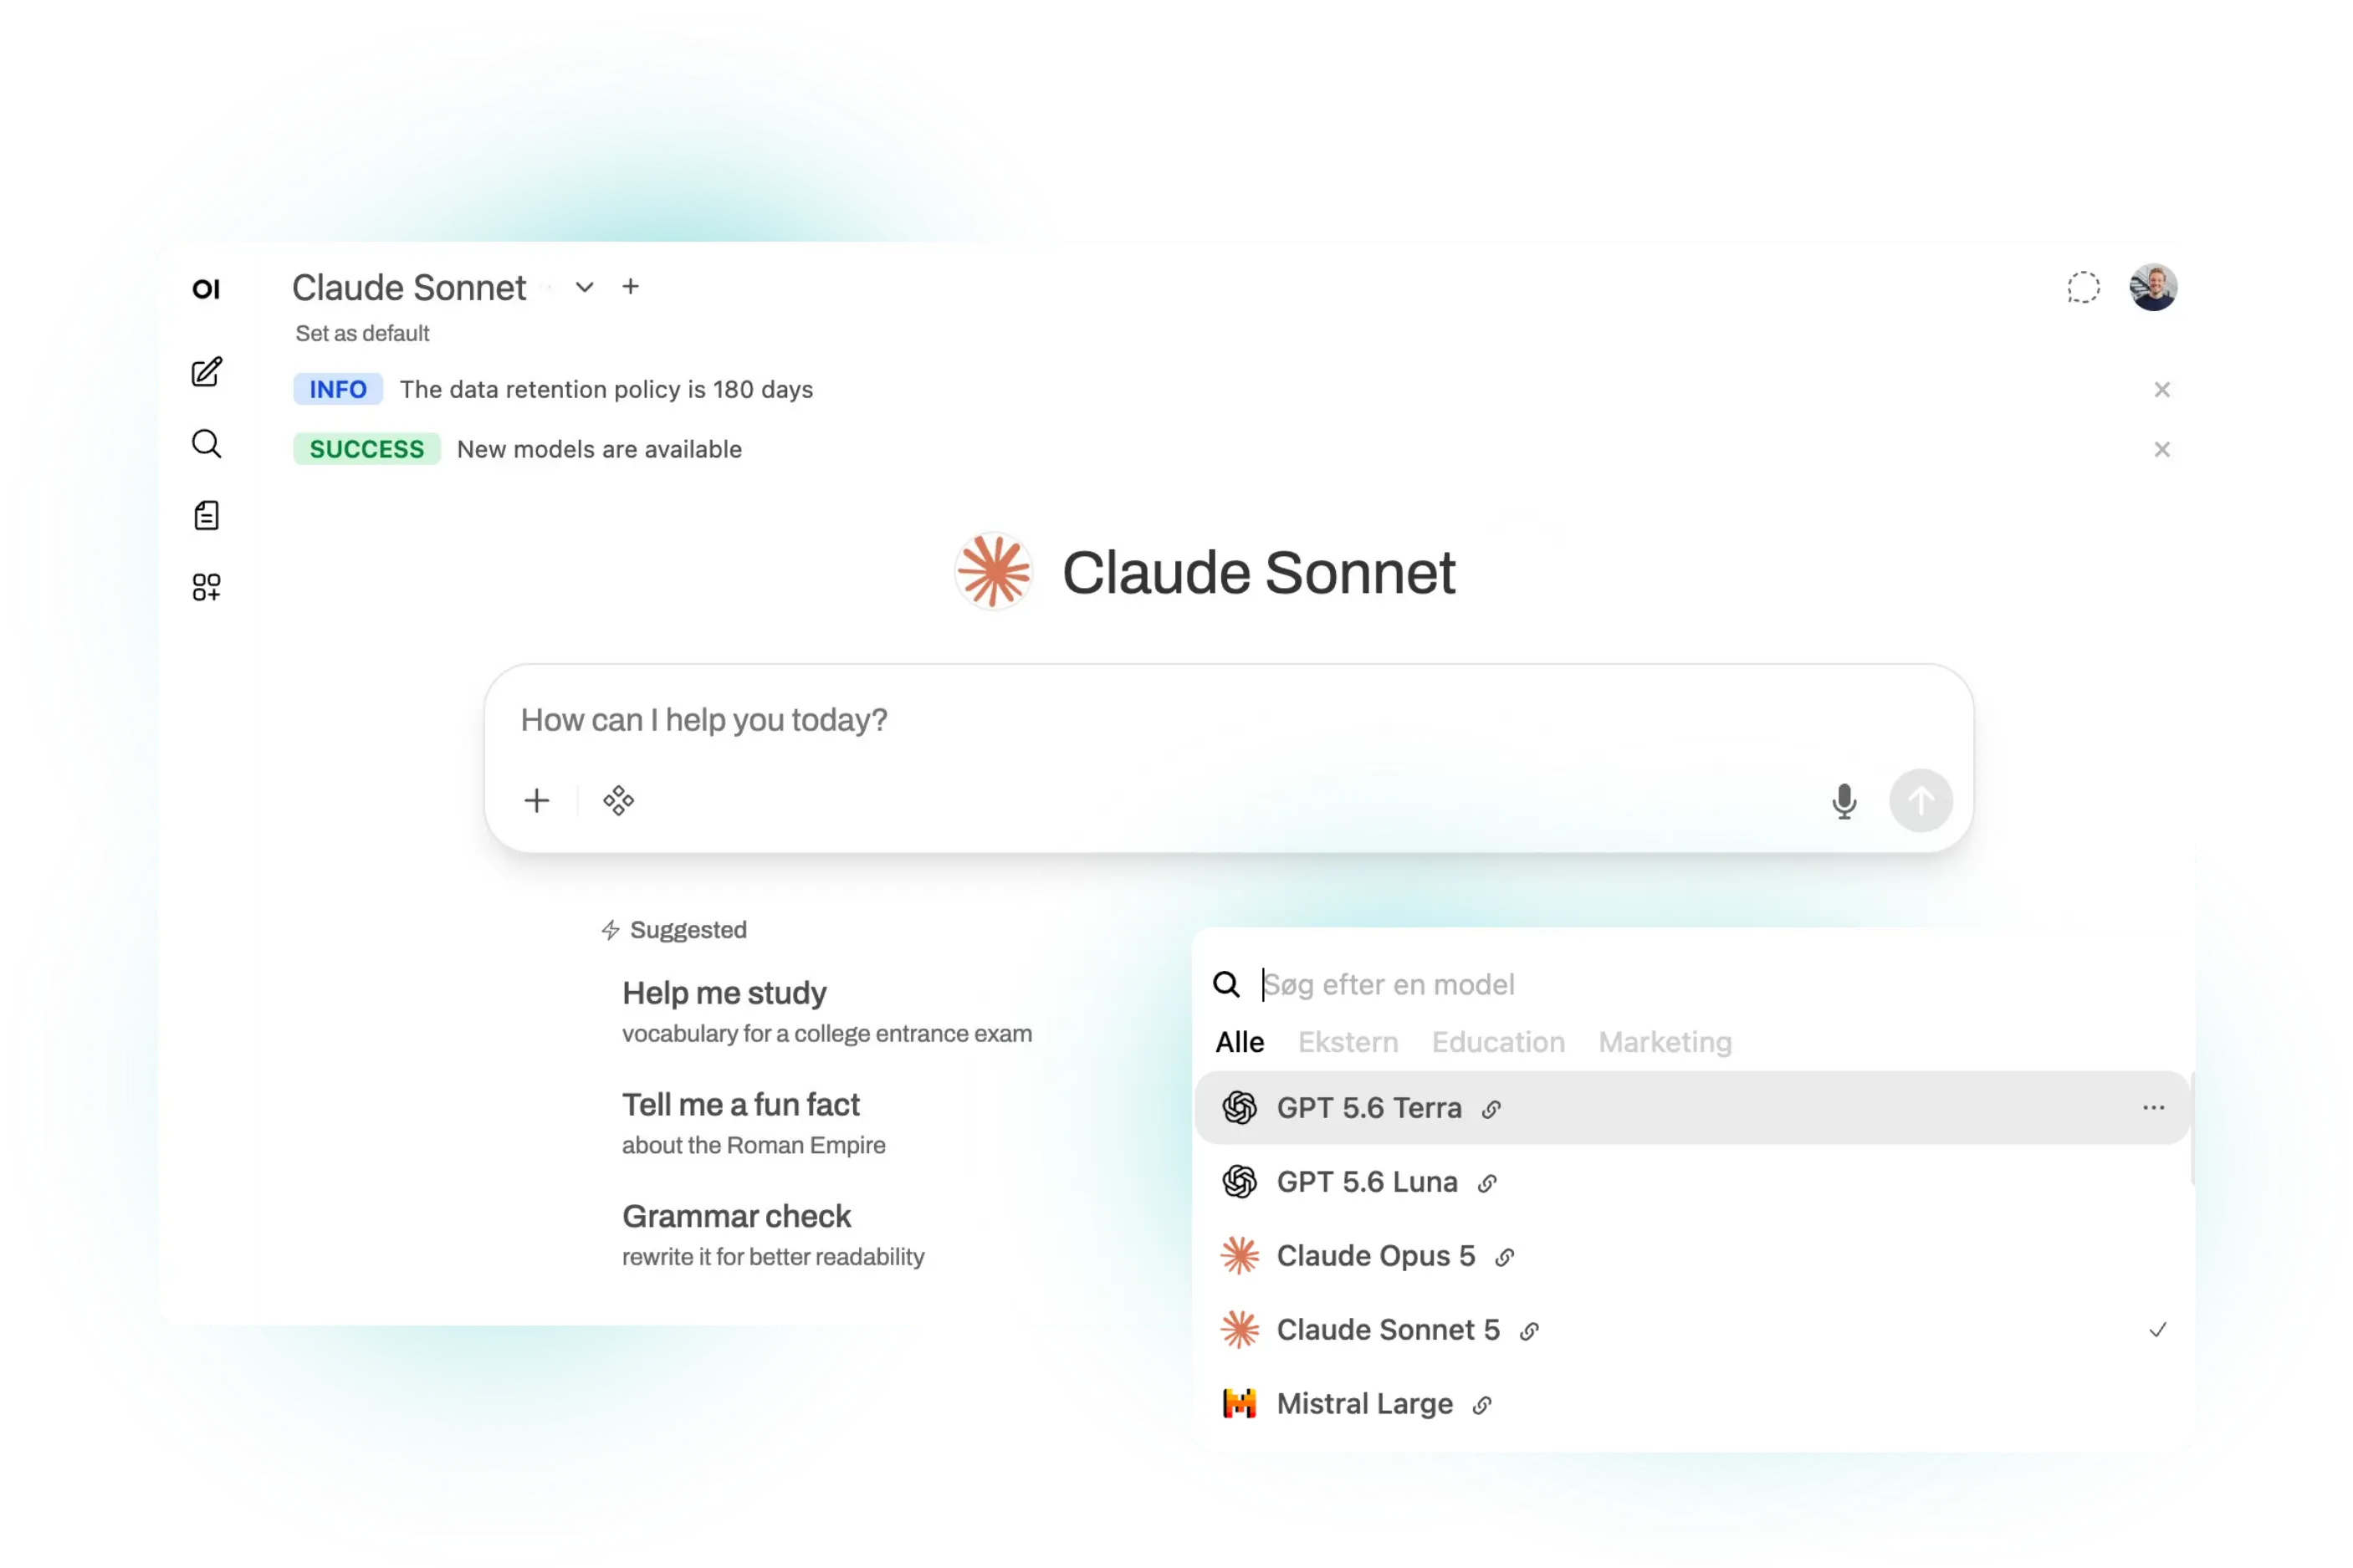
Public institutions can't afford to send citizen data to tools they don't control. GRACE GenAI closes that gap with a secure chat built for the public sector, hosted in Europe or on your own infrastructure, and designed to meet GDPR and EU AI Act requirements from day one.
Your employees get a tool they'll use. You keep full control.
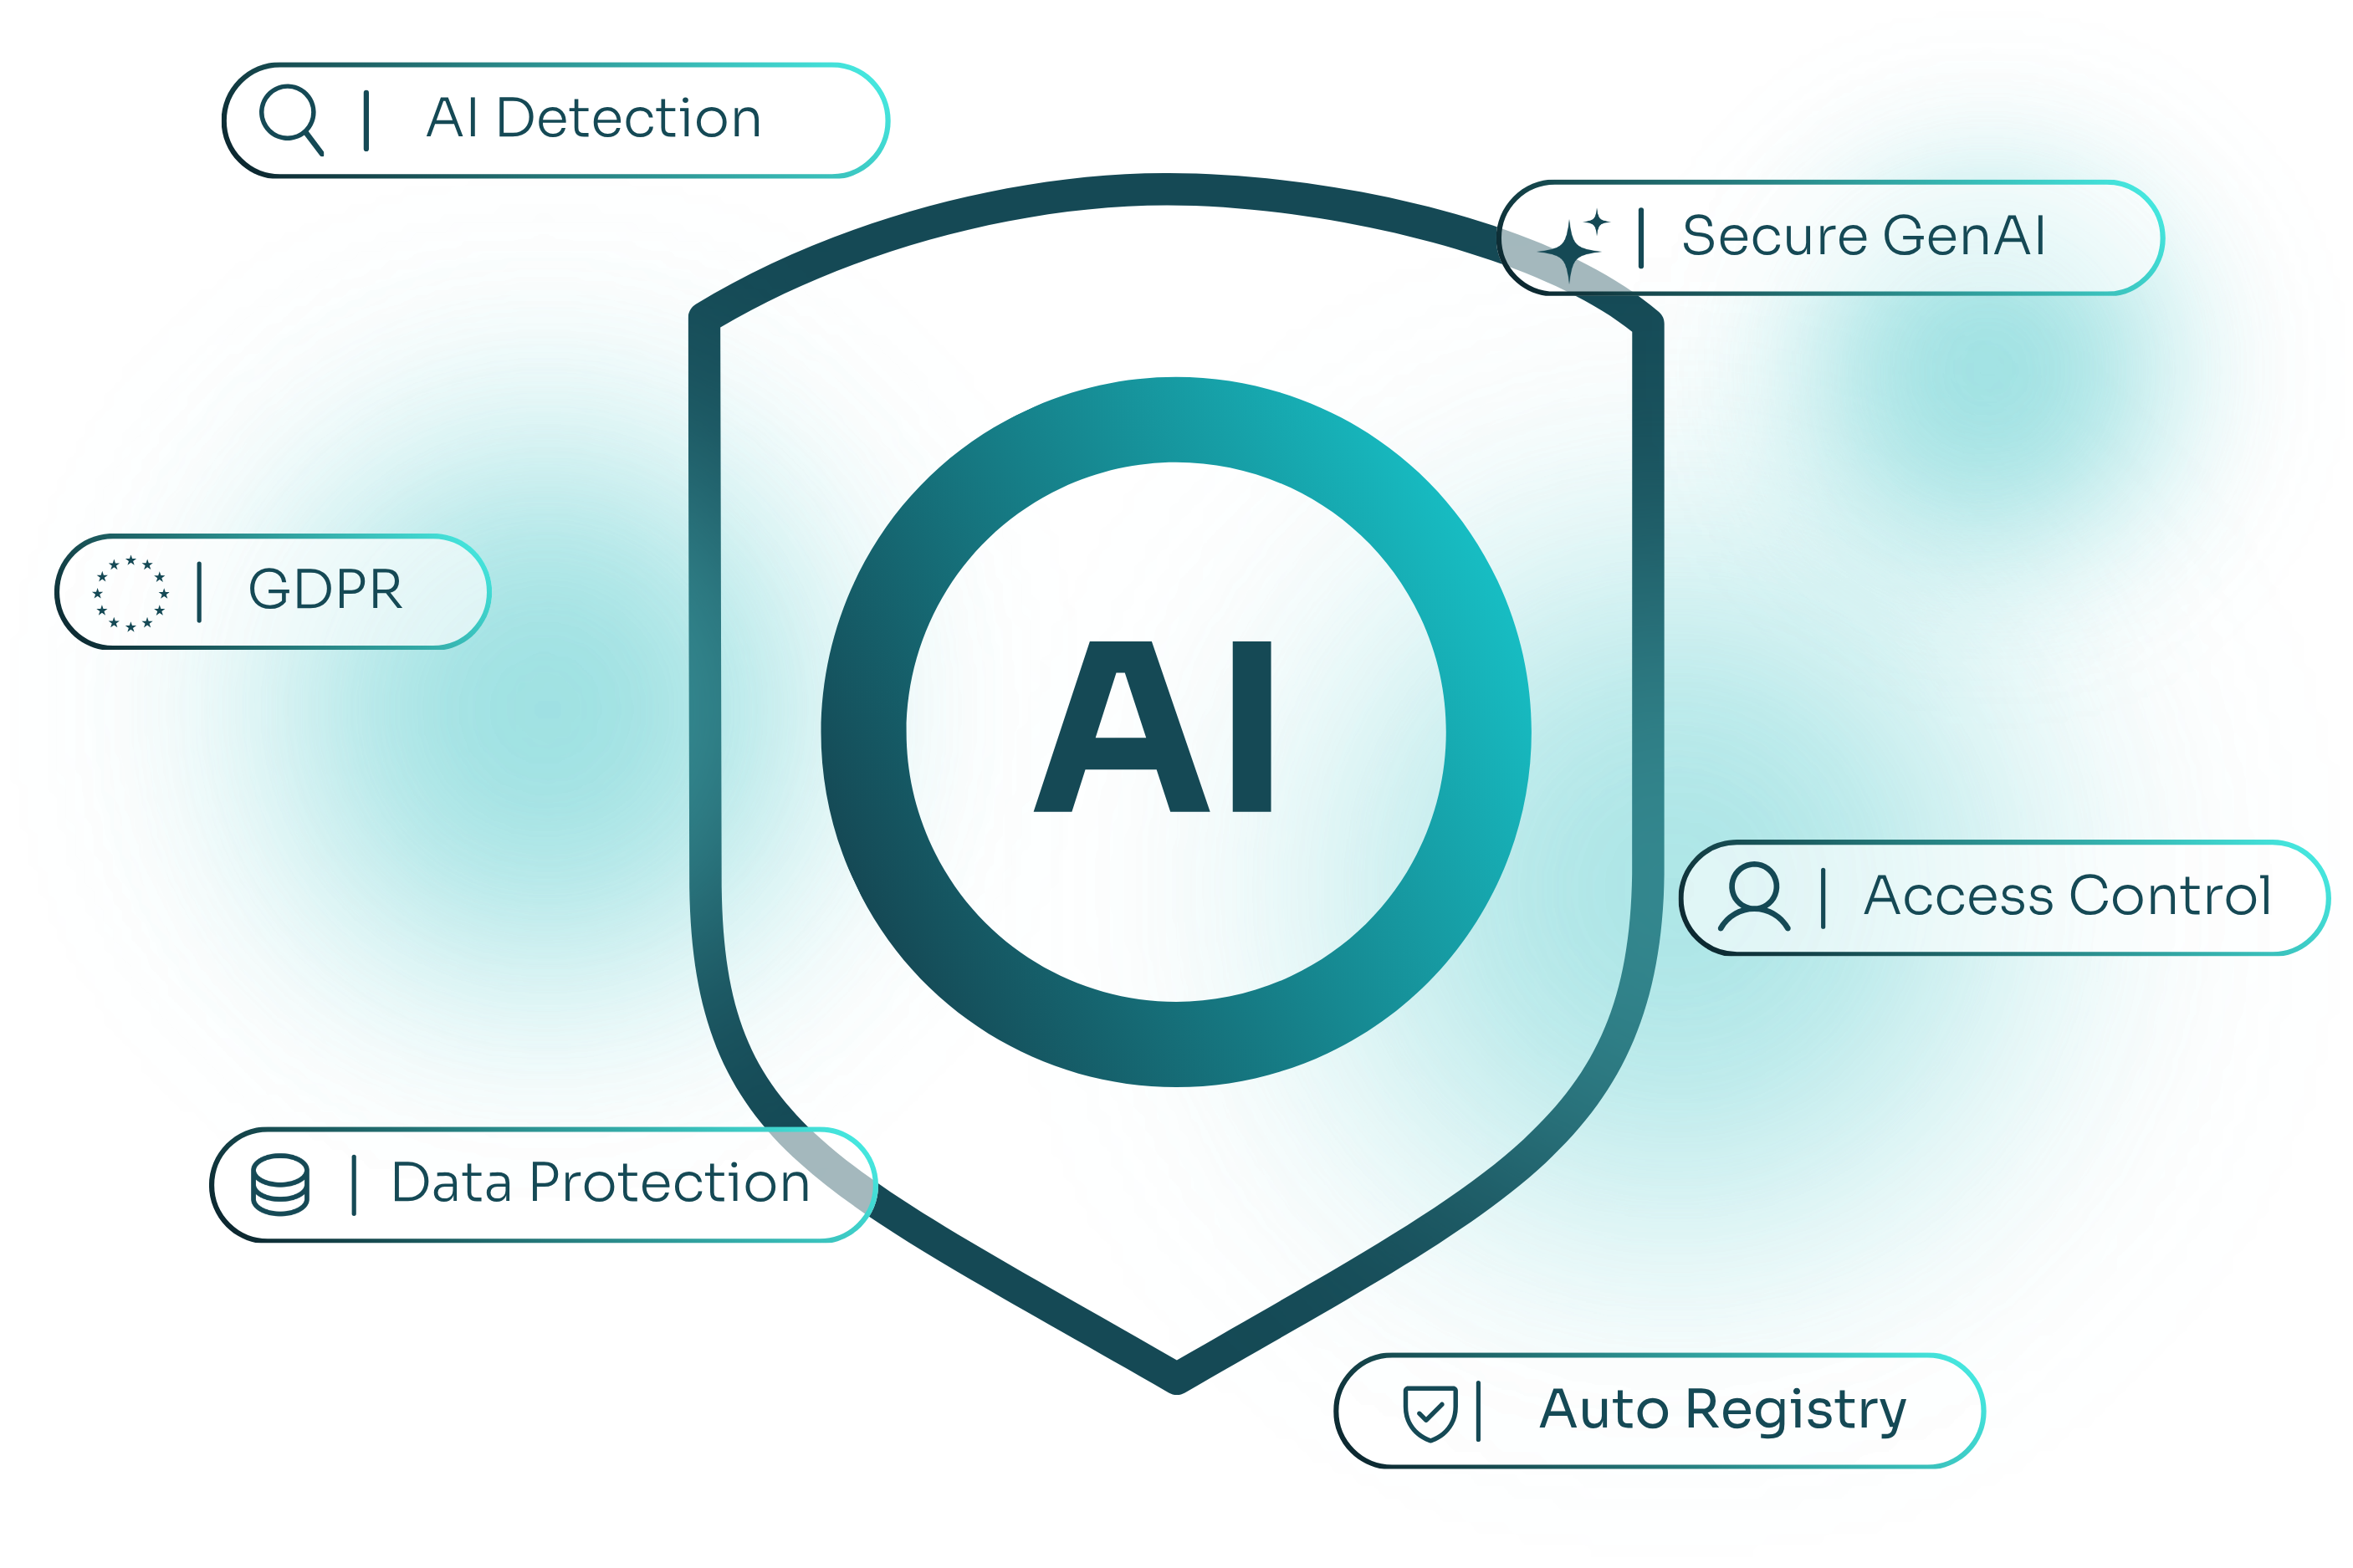
Across public institutions, employees are already using AI tools that IT never approved, often with citizen data. GRACE detects every AI system in use, including Shadow AI, and autoimatically register it with our AI Auto Registry.
From there, you set the rules: who can use what, with which data, and under which EU AI Act obligations. The result is full oversight of your AI landscape and a clear record you can show auditors, politicians and citizens.

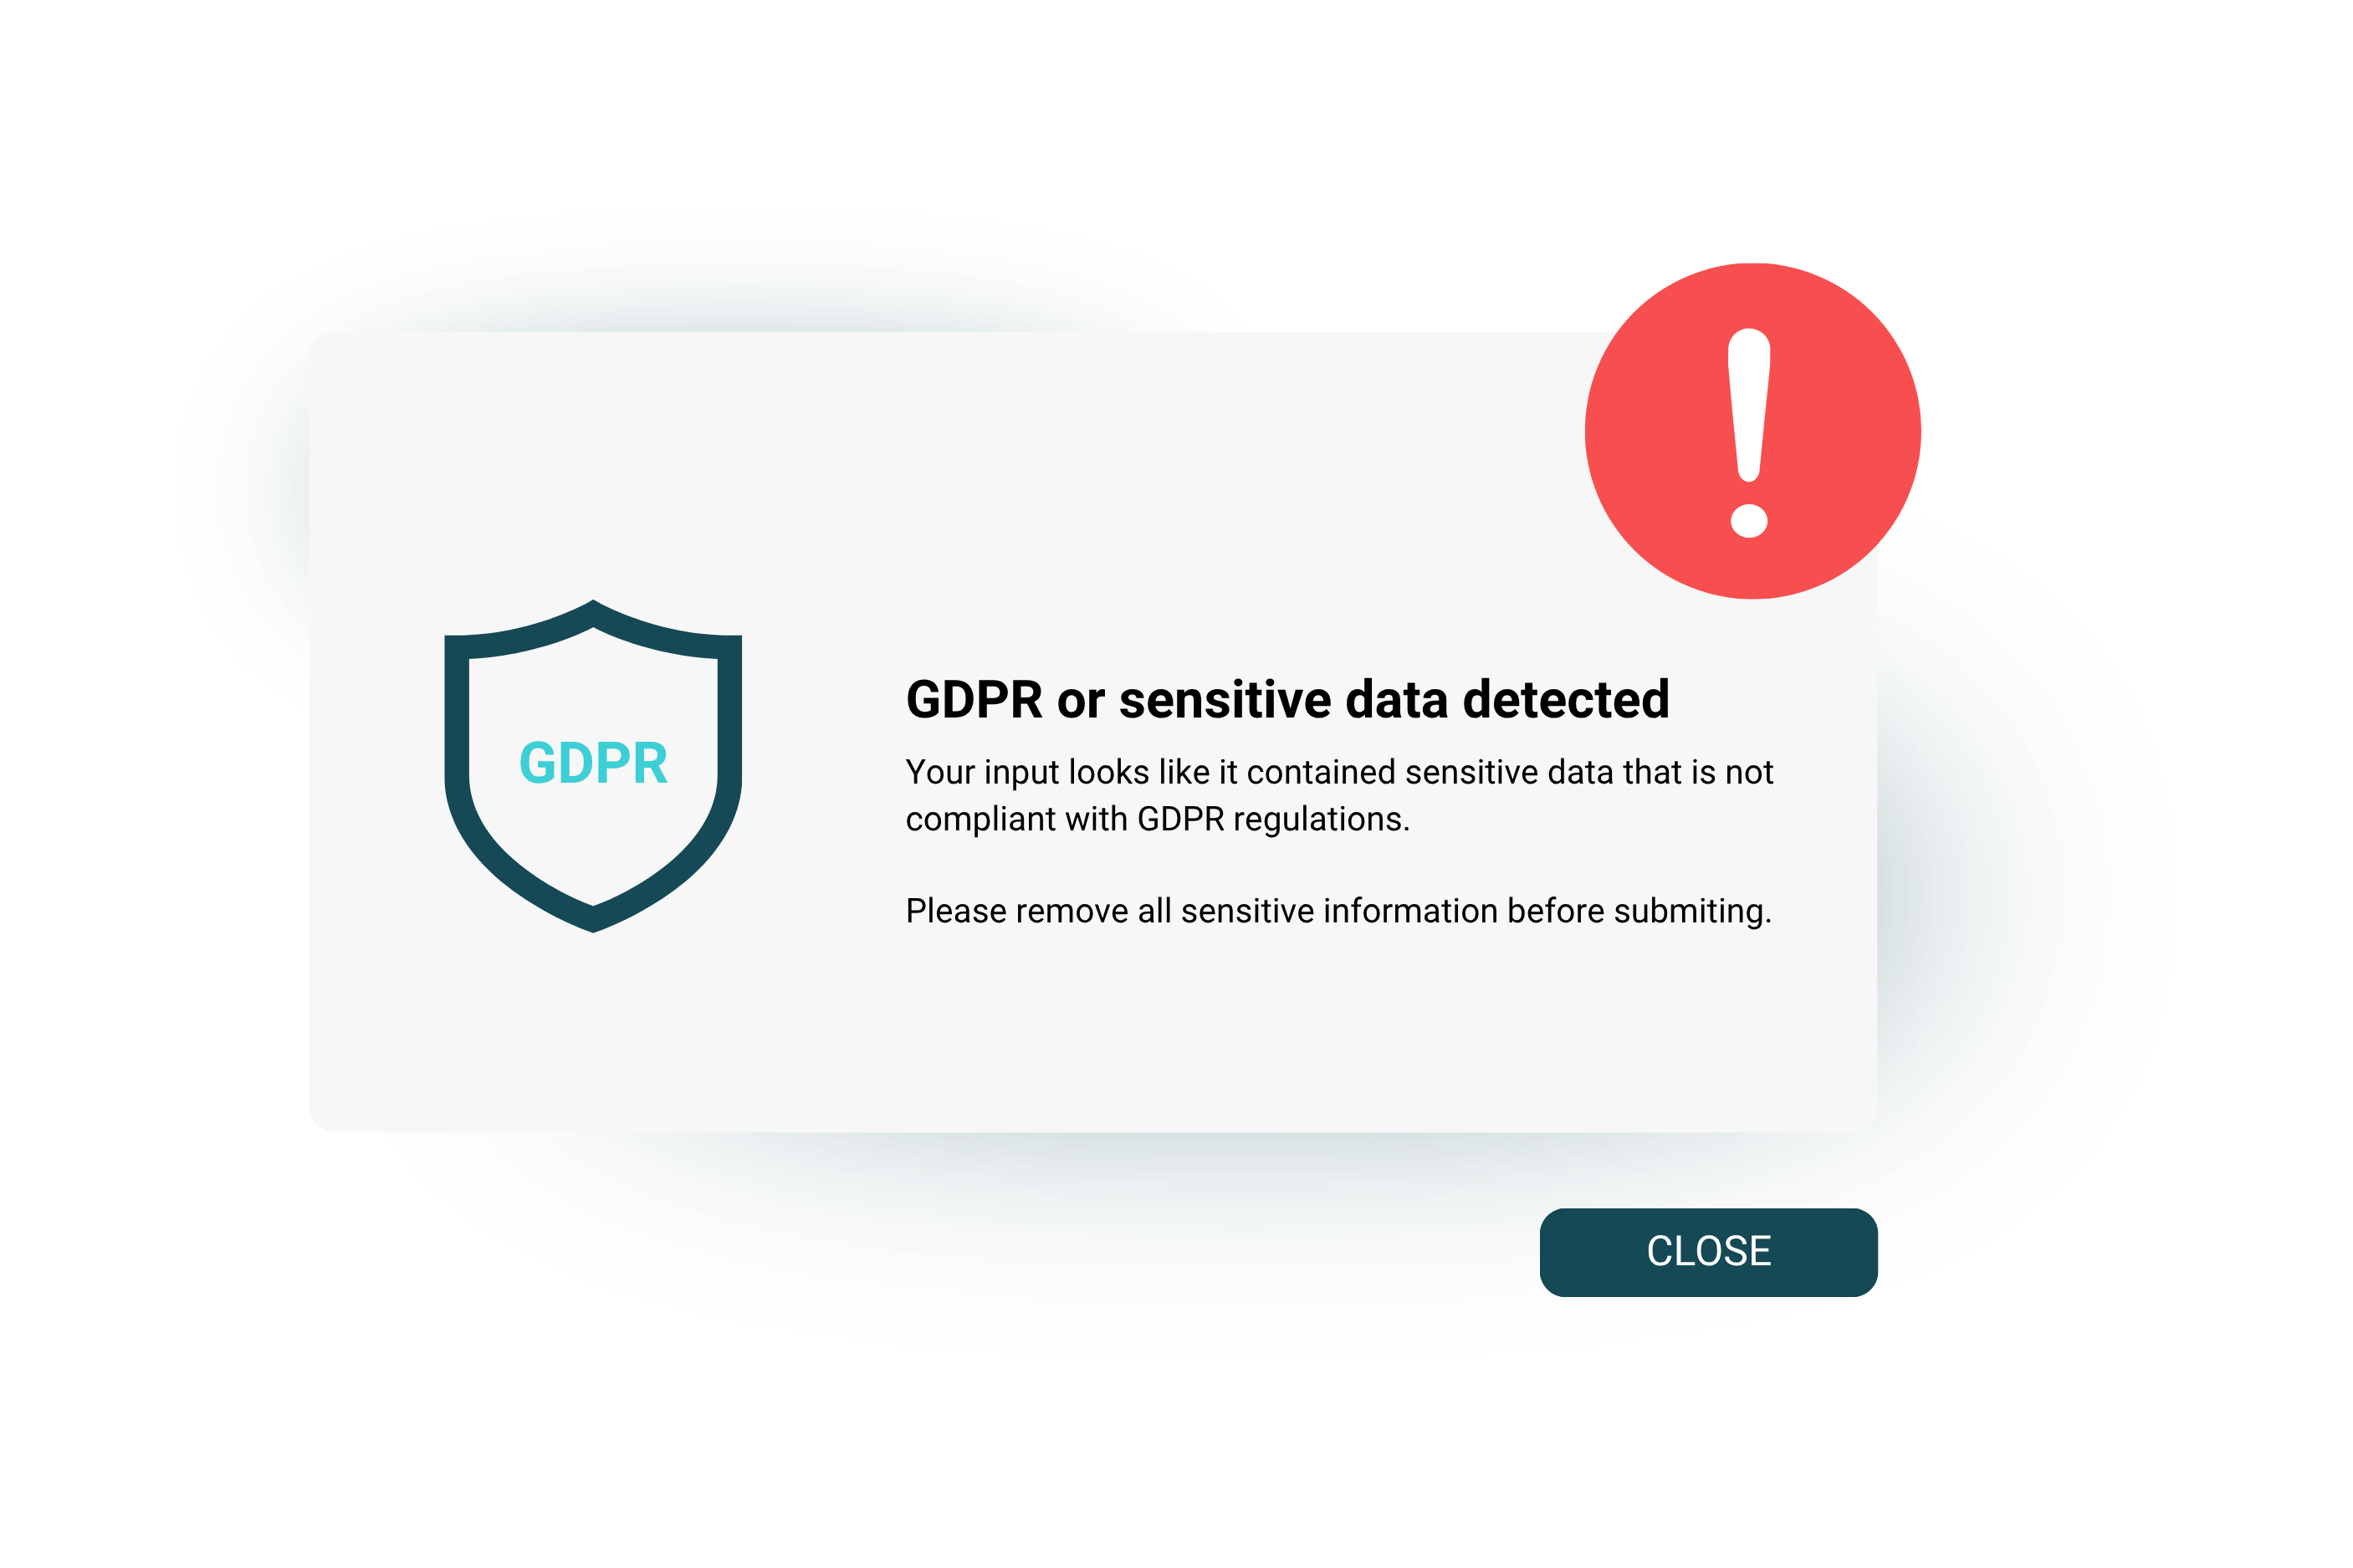
One pasted CPR number in the wrong AI tool is a GDPR breach. GRACE protects public sector institutions by detecting personal and sensitive data, like CPR numbers, health information and case details, before it reaches the AI model.
You decide what happens: block the prompt or warn the user. Every rule is configurable to your institution's risk level, so each department can use AI safely under its own data protection policy.
Every new AI tool in a public institution needs a Data Protection Impact Assessment (DPIA), and each one can take months of manual work. GRACE cuts that workload by documenting your AI systems automatically: which models are in use, what data they process and which safeguards are in place.
That documentation feeds directly into your DPIA, so your data protection officer starts from a complete overview instead of a blank template. The result is faster GDPR compliance and more time for the assessments that actually need human judgment.
AI risk doesn't end when a system goes live. GRACE supports public sector institutions at every stage of the AI lifecycle: from assessing a new use case and documenting risks, through approval and deployment, to ongoing monitoring and eventual retirement.
Each step is recorded, so you always know who approved what, when and on which basis. That gives you a complete audit trail for every AI system and makes EU AI Act compliance part of how you work, not a task you catch up on later.

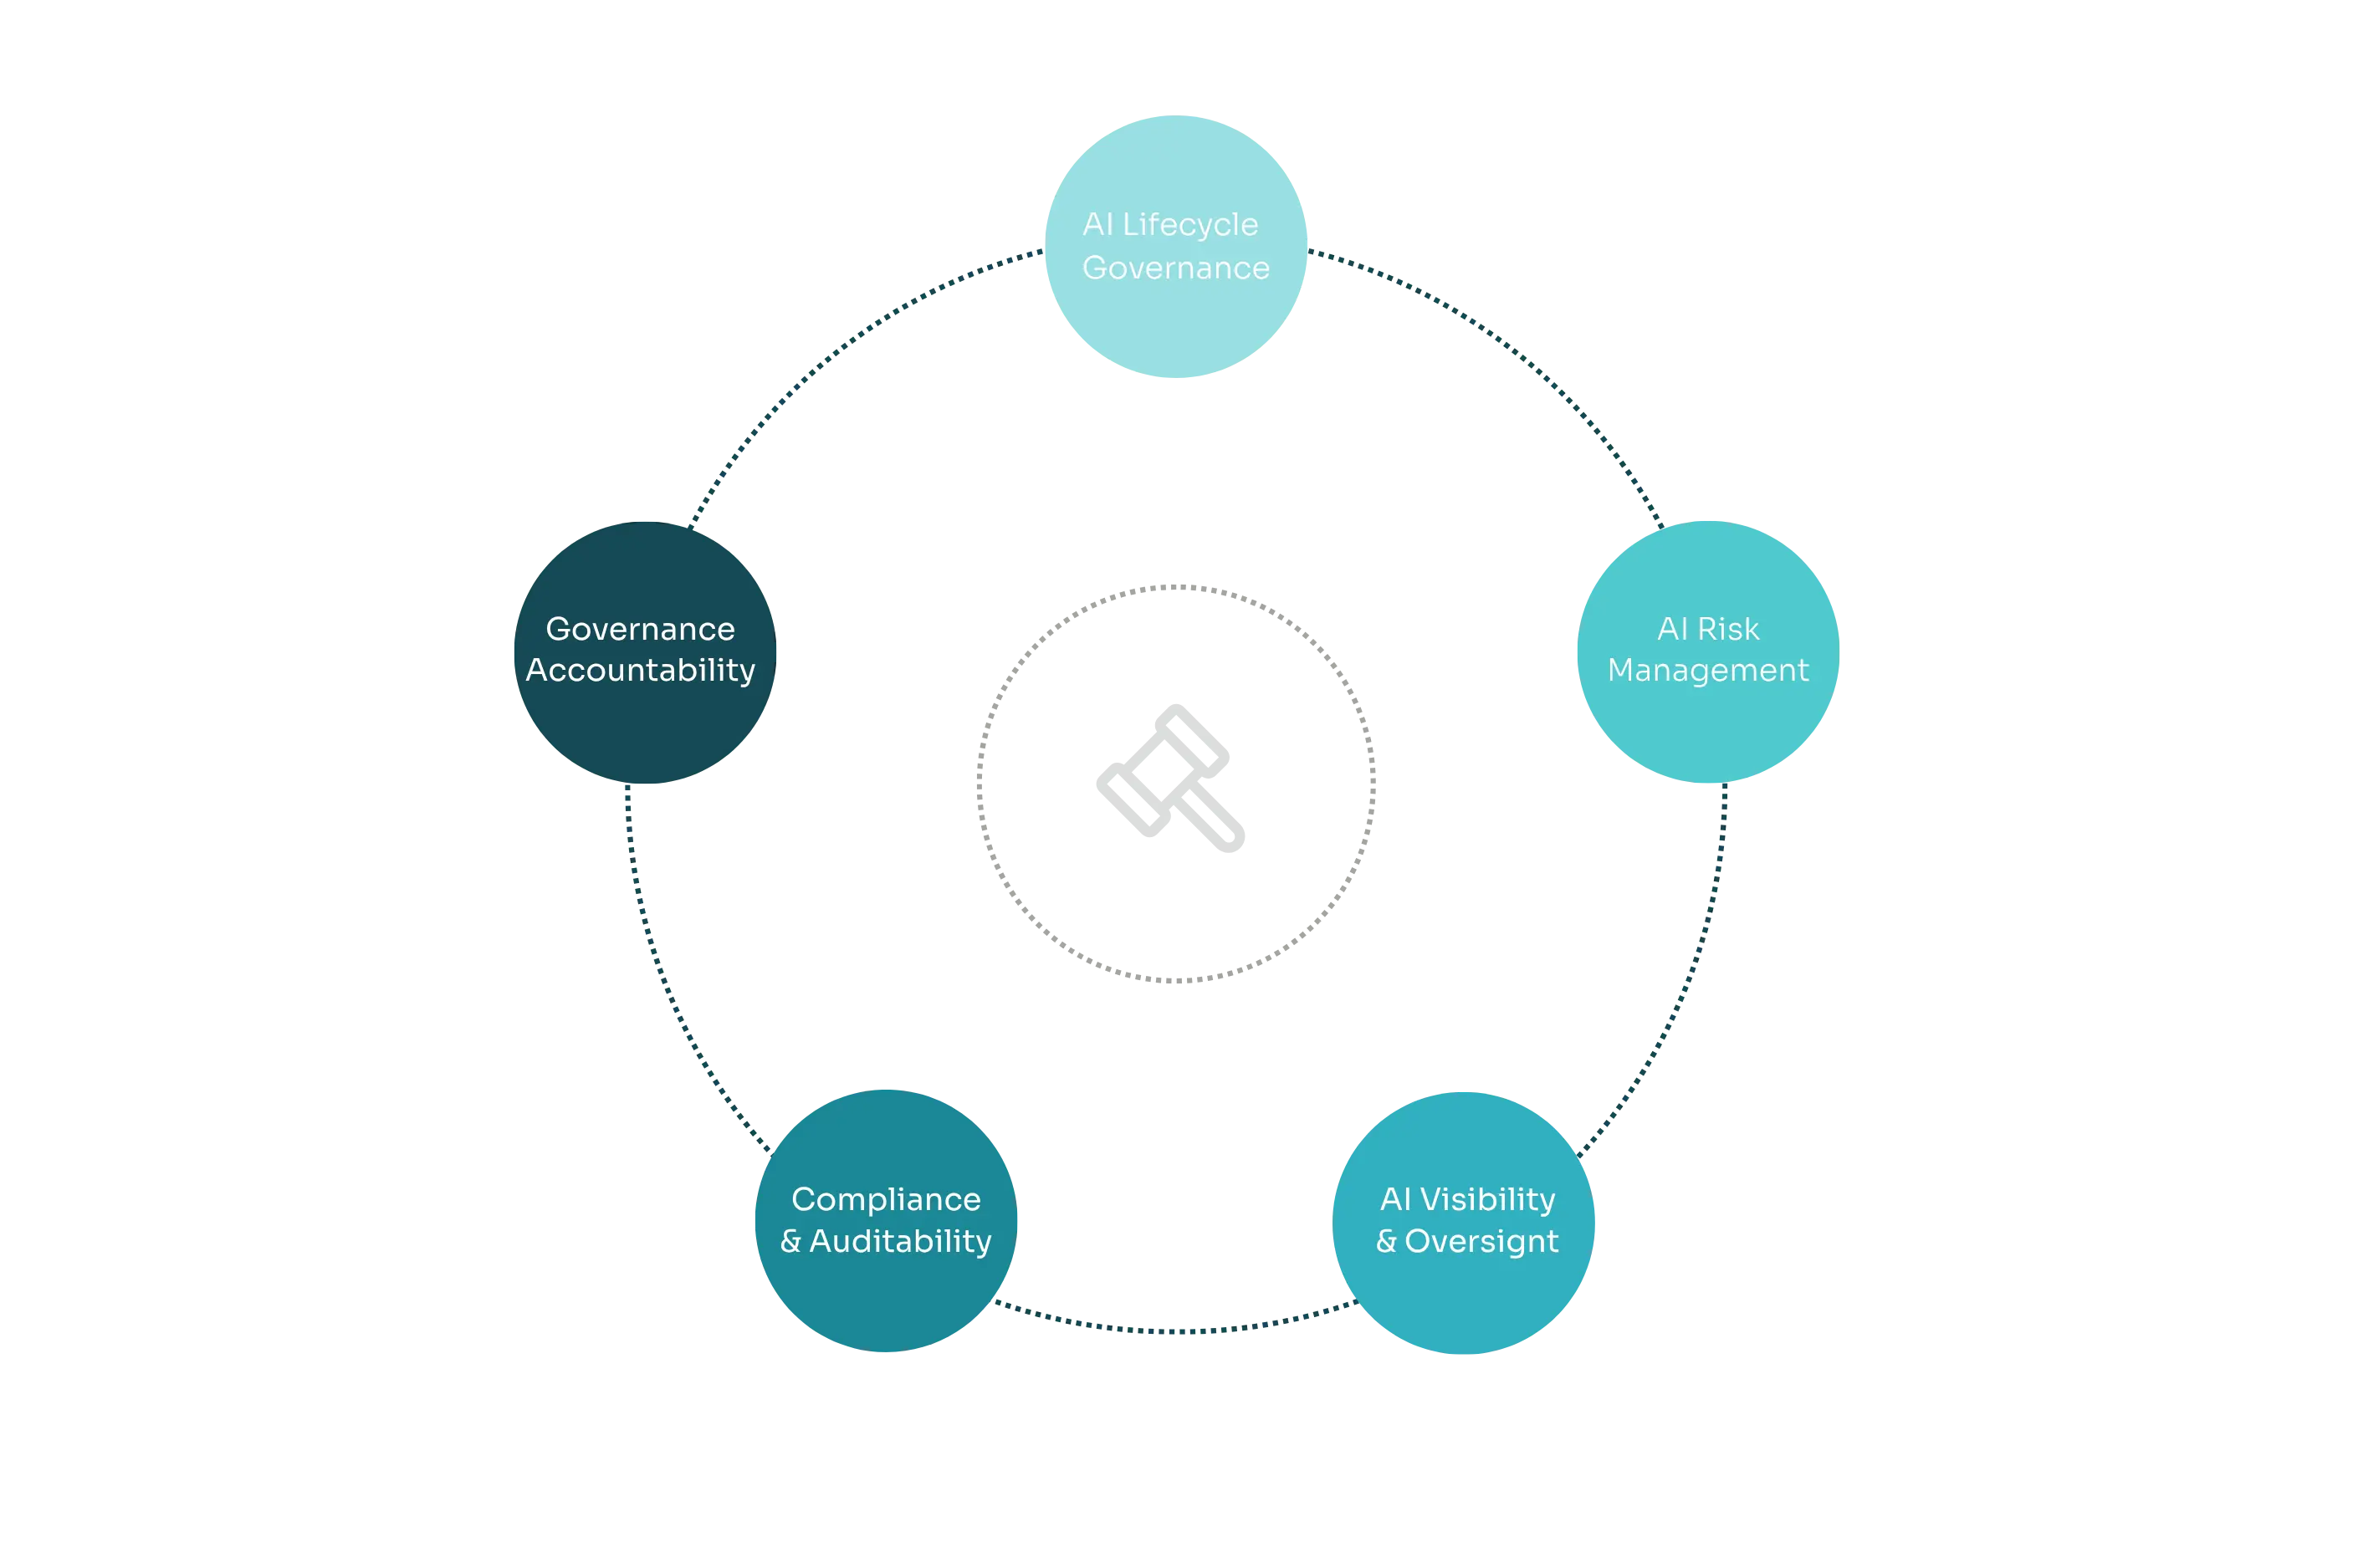
Beyond the out-of-box AI infrastructure, GRACE offers three modules, enabling organisations to succeed with all AI operations. Modules can be integrated into your existing solutions individually.
Discover the GRACE AI Platform


GRACE is an amazing platform for data scientists - it has everything you need unified in one place, being intuitive and user-friendly.

GRACE is an intuitive and efficient platform that helped streamline our AI implementation from end-to-end. By simplifying the deployment process, it enabled our data scientists to dedicate more time to their core tasks and less to operational complexities.

Together with 2021.AI we are creating some of the most advanced and ambitious forecasting models for the shipping industry.

With the abundant data we have, we decided to work with 2021.AI to analyze how modern AI techniques can support our clients in increasing the resuls of their fundraising efforts.

We pride ourselves on innovation - a trait shared by 2021.AI, who are well positioned to help us fast-track our work with AI and Machine Learning. We have seen strong potential from our initial collaborations, and the next step for us is not to evaluate and assess.

We went from challenge to implementation and actual cost savings in a very short time span. The collaboration with 2021.AI showed us that AI is the key for Spar Nord to remain competitive in the future.


Working with 2021.AI has been both effective and a very positive experience. Their strong focus on Responsible AI and governance made it possible for us to build a solution we and the users can trust — and making complex health data easier to access and understand for patients, professionals, and the public.

Our healthcare system is under significant pressure, and that pressure will only grow in the future. We need to think innovatively. With solutions like the chatbot, we aim to ease some of the strain and ensure that every patient receives equal care.
Leave your contact details, and we will connect to set up an introductory meeting.